


How to Enable Root SSH on Debian/Ubuntu Servers
Why Enable Root SSH Login?
Allowing SSH root access gives you full control over your server. Here are the main benefits:
- Manage files and folders – edit or back up system directories that normal users cannot access.
- Simplify maintenance and troubleshooting – install services, update packages, or fix configuration issues.
- Support automation and scripts – run cron jobs and tasks that require full root privileges.
Important:
Enabling root SSH increases security risks. Always use a strong password, consider changing the SSH port, and configure firewall rules.
Steps to Enable Root SSH on Debian/Ubuntu
Step 1: Log in to the Server
Use a regular user (e.g., administrator) to connect via PuTTY or your SSH client.
ssh administrator@your-server-ip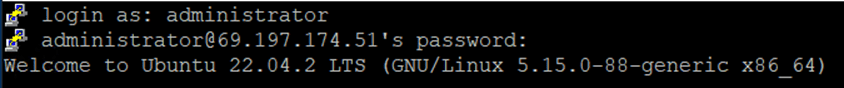
Step 2: Switch to Root User
Run the following command and enter your password:
sudo -i
Step 3: Set Root Password
Create and confirm a root password:
passwd root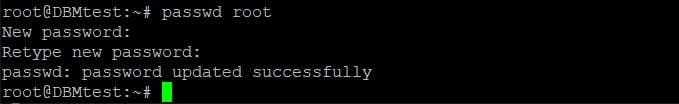
Step 4: Edit SSH Configuration
- Open the SSH config file:
nano /etc/ssh/sshd_config- Find this line:
#PermitRootLogin prohibit-password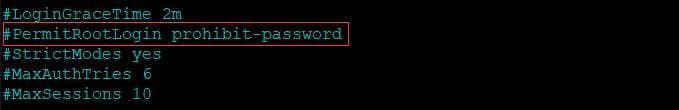
3. Remove the # and change it to:
PermitRootLogin yes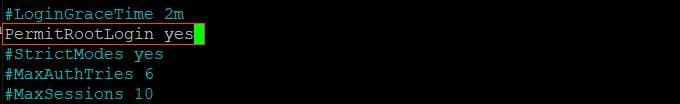
4. Save and exit (Ctrl + X, then Y, then Enter).
Step 5: Restart SSH Service
Restart the SSH service so changes take effect:
sudo systemctl restart ssh
For Ubuntu 24 early releases, if the above fails, run:
sudo systemctl daemon-reload
sudo systemctl restart ssh.socket
Step 6: Test Root SSH Login
Open a new SSH session and log in with:
ssh root@your-server-ip
Enter the root password you set earlier. You now have SSH root login enabled!
Optional: Secure Root SSH Access
Since root login via SSH can be risky, we recommend:
- Change SSH port from
22to something above1024(e.g.,1217): How to change the SSH port - Use firewall rules to allow only trusted IPs.
- Use SSH keys instead of passwords for stronger security.